Find the weak point before someone else does.
Penetration testing, QA and network care. Written authorization before we start, a retest after you fix.
Invoicing app: web application and API
- Target
- app.invoicing.test, /api/*
- Authorization
- Signed before any test traffic
3. Findings
- F-01Org A user can edit Org B invoices (IDOR)
- F-02No attempt limit on the login endpoint
- F-03Session cookie sent without the Secure flag
- F-04Server version shown in response headers
Who we have worked with
Siddhartha Cable Car
Network setup and upkeep: MikroTik, Cisco, Cambium, servers.
Kathmandu University School of Education
Server security and maintenance.
National Examinations Board
Supported their systems.
Networks we set up and look after.
Two internet lines, one firewall, a VLAN for each kind of device, and on-site servers we patch and back up.
Managed network and server careStock photos of the kind of hardware we support, not photos of client sites.
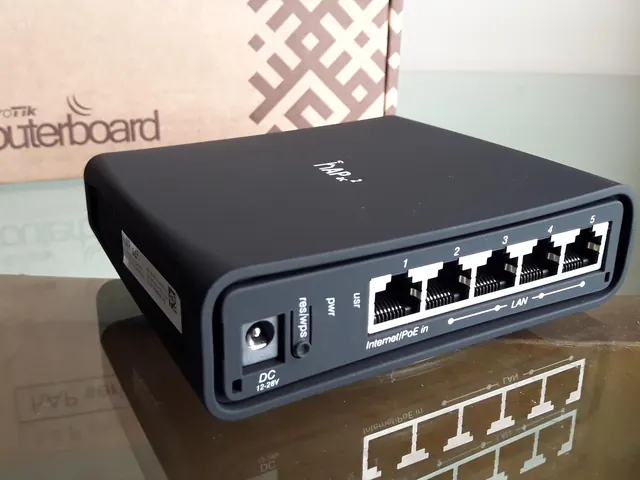
MikroTik routerPhoto: Uhernandez, CC BY 3.0 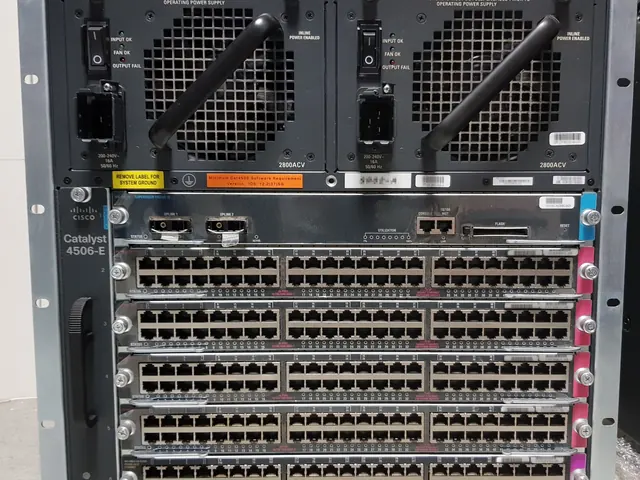
Cisco Catalyst switchPhoto: X-Javier, CC BY-SA 4.0 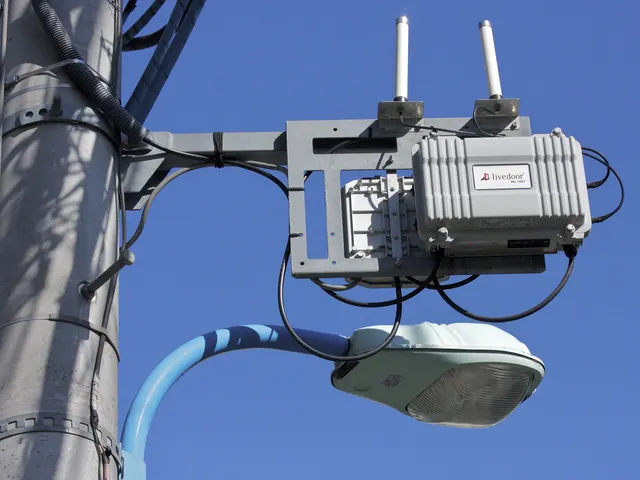
Outdoor Wi-Fi access pointPhoto: Maripo GODA, CC BY-SA 3.0 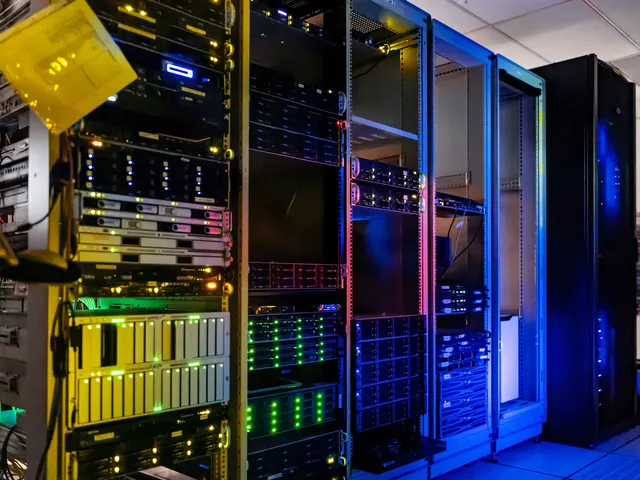
Servers in racksPhoto: NOIRLab/NSF/AURA/T. Slovinský, CC BY 4.0


What does EK Securities do?
EK Securities is the security testing and QA wing of EK Ra Sunya Inc. It is not a securities or investment business. We test web apps, APIs, mobile apps, networks and servers for the weak points an attacker would use, with evidence, a fix and a retest for each. We also set up and maintain networks, servers and deployment pipelines.
Services
All servicesWeb and API VAPT
Login, sessions, roles, business logic and every API route behind your web app.
Mobile app VAPT
The Android and iOS build you ship, and the API it talks to.
Network and infrastructure assessment
What is exposed to the internet and the office network, and what an attacker could reach from there.
Cloud and server hardening review
Linux servers, containers, cloud accounts and the CI that deploys to them.
QA and test automation
Manual QA before a release, and automated tests that keep catching the same bugs after it.
Run and maintain
Managed network and server care
Internet from more than one provider, a separate VLAN for each kind of device, and the on-site servers behind them, set up and kept patched.
DevOps and deployment pipelines
Automated deploys, a hardened edge, tested backups and monitoring for the apps you run.
Ongoing security operations
Watching new vulnerabilities, patching on a schedule and keeping access tidy, month after month.
Findings map to public standards.
From scope to retest, in writing.
How each step worksScope
We agree what is in and out: hosts, apps, roles, test accounts, environments and the hours testing may run.
out: written scope
Authorize
The system owner signs a written authorization before any test traffic is sent. No signature, no testing.
out: signed authorization
Test
Manual testing backed by tools. Every finding is confirmed by hand. A critical issue is raised as soon as it is confirmed, not saved for the report.
out: findings confirmed by hand
Report
Each finding with severity, where it is, the evidence, the impact and a fix your developers can apply.
out: report with evidence and a fix each
Retest
Once you have fixed the findings, we test them again and update the report to show what was closed.
out: report updated: closed or still open
What does the report look like?
Same six parts every time: a developer can reproduce it, a manager can rank it.
Read the sample report- Severity
- High
- Where
PATCH /api/invoices/{id}- Issue
- Any signed-in user can edit another organisation's invoice by changing the id (IDOR).
- Evidence
- The request and response showing user A's session changing an invoice owned by user B.
- Fix
- Load the invoice scoped to the caller's organisation and return 404 when it does not match.
- Retest
- Same request repeated after the fix, result recorded in the report.
We test our own software first.
Ek Ra Sunya builds and runs these. We test them the way we test yours.
Questions
Do you test production systems?
Only when production is in the signed scope. We prefer a staging copy. On production we agree a test window, use dedicated test accounts, and never run denial-of-service or destructive tests.
Do you need our source code?
No. We can test from the running application and test accounts. Read access to the code helps us trace a behaviour to the exact line and usually finds more in the same time, so we ask for it when you can share it.
Is EK Securities a securities or investment company?
No. EK Securities is the security testing and QA wing of EK Ra Sunya Inc. It is not a securities or investment business. It does not deal in shares, bonds or any financial product.
Who is behind EK Securities?
EK Securities is a brand of Ek Ra Sunya Inc Pvt. Ltd., a software company in Lalitpur, Nepal, that builds and runs EK ERP, EK SMS and EK Cloud.
Tell us what you want tested.
A short call, then a signed scope. No testing before that.